Documentation base URLs use placeholder https://{your-tenant}.sso.id. Log in to show your tenant or custom domain.
Log in for Your Tenant URL
Chapter 1 — Identity Onboarding & End-User Portal

Account Lifecycle & App Launcher Experience

Before an enterprise admin configures their first application — or an employee launches their daily SaaS tools — every identity journey starts with the SSO.ID v2 Account & Workspace Portal. Discover how registration modes, the Google-style Multi-Account Switcher, the Okta-style App Launcher, Passkey enrollment, and GDPR self-service privacy work end to end.

Chapter 1 Story: Two Faces of the Same Portal

Why SSO.ID v2 Adapts Automatically to Admins vs. End Users

At CloudPulse, two people sign into https://{your-tenant}.sso.id on Monday morning:

  • Maya (Platform Security Architect): Signs in and lands on the Admin Console ( /overview), where she switches between the CloudPulse Production (US) and CloudPulse Europe (EU) tenants, inspects real-time login telemetry, and manages applications.
  • Liam (Customer Support Specialist): Signs in and lands on the End-User App Launcher — a clean, distraction-free workspace showing chiclets for every application he is authorized to use (CRM, Billing Desk, Analytics), complete with custom sections, one-click SSO launch, self-service Passkey registration, and active device session controls.
Key Architectural Insight: When a user owns or is a member of a Tenant (or holds administrative menu permissions via /api/tenants/{tenantId}/roles/user-menus), they can toggle seamlessly between the Admin Console and the User Portal using the top-bar mode switcher.
1. Four Ways Identities Enter SSO.ID v2

Depending on your tenant security policy ( /settings → General & Registration), users can onboard through four distinct flows:

A. Public Self-Service Registration (allowSelfRegistration)

Ideal for B2C and PLG SaaS apps. Users sign up with First Name, Last Name, Email, and Password (validated live against your Tenant Password Policy), then verify their email via a signed token or OTP (enableEmailVerification).

B. Admin & Organization Invitation Flow

Ideal for B2B and zero-trust teams. Self-signup is disabled; admins invite users via /user-management (POST /api/users/invite) or /tenant-members. Invitations can be resent anytime via POST /api/users/{userId}/resend-invite.

C. Just-in-Time (JIT) Social & Enterprise Federation

When a user authenticates via Google, GitHub, Microsoft Entra ID, or Okta SAML/OIDC and autoProvisionUsers is enabled on the Connection, SSO.ID automatically provisions their account and maps their external groups to SSO.ID Roles.

D. Automated SCIM 2.0 HRIS/IdP Provisioning

Enterprise workforce directories push users and groups into SSO.ID ahead of time via POST /api/scim/v2/Users so accounts and permissions are ready before the employee's first login.

2. The End-User App Launcher Portal

When end users sign into https://{your-tenant}.sso.id (or your custom domain), the portal calls GET /api/users/current/applications and renders an interactive Application Chiclet Grid:

Flow Diagram Region-Routed Universal Login & App Launcher Flow
flowchart LR L["Universal Login (/login)"] --> D["Email / Home Region Lookup (US or EU)"] D --> A["Tenant Auth Portal (/auth/Account/Login)"] A --> M{"MFA / Passkey Required?"} M -->|"Yes"| C["Verify Passkey / TOTP / OTP"] M -->|"No"| P["App Launcher (/app)"] C --> P P --> S["One-Click Launch to OIDC / SAML App"]
Users are automatically routed to their US or EU tenant portal, authenticated with adaptive MFA, and presented with their assigned apps.
1

One-Click SSO Launch & Custom Sections

Users can click any assigned Application tile to immediately initiate an OIDC/OAuth2/SAML login into that app without re-entering credentials. Users can also organize their apps into custom folders/sections (persisted per user/tenant), search apps in real time, and pin frequently used apps.

2

Request Access to New Applications & In-App Notifications

If an employee needs access to an application they aren't yet assigned to, they can submit an App Access Request directly from the portal, triggering a real-time notification in the top bell menu (/api/notifications) for tenant administrators.

3

9-Language Localization (with RTL), Dark Mode & Voice Commands

The top navigation bar supports instant switching between 9 languages (English, Arabic with automatic Right-to-Left dir="rtl" layout, Chinese, Dutch, French, German, Italian, Spanish, and Turkish), persistent Dark/Light themes, and a hands-free Voice Command Assistant (Web Speech API) so admins can say "Go to Applications" or "Open Audit Logs".

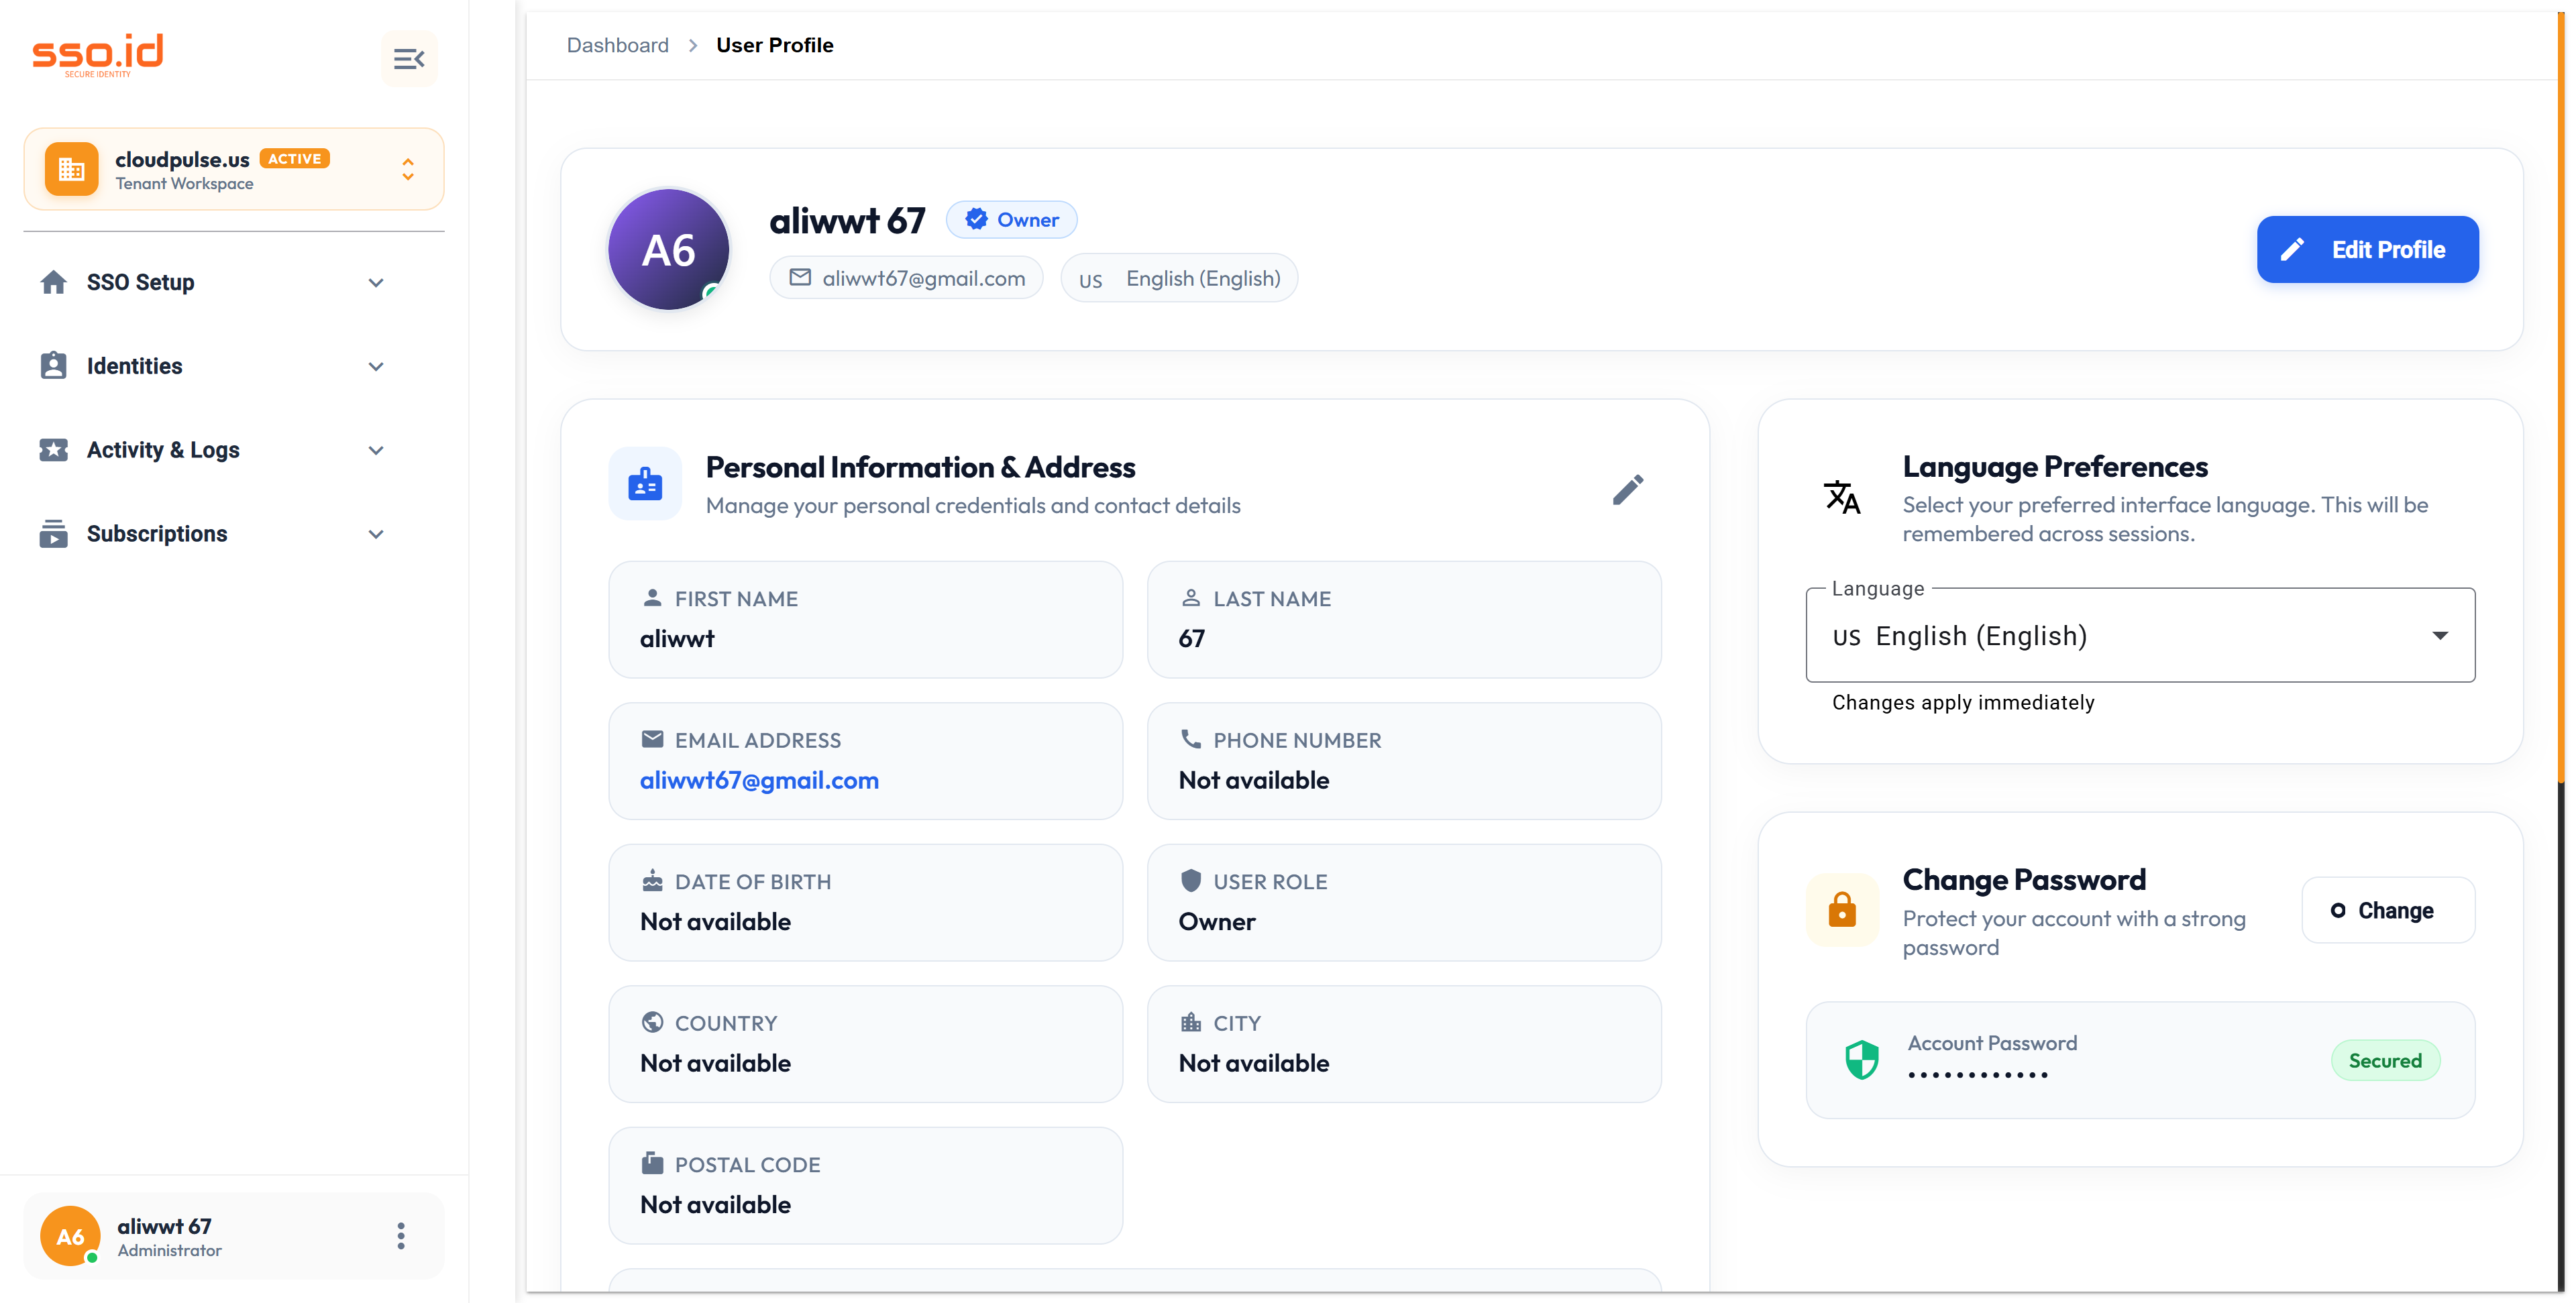
https://cloudpulse.us.beta.sso.id/user-profile Click to zoom
Self-Service User Profile, Password Management, Language Preferences & GDPR Privacy Controls.

3. Multi-Account Switcher & Multi-Tenant Workspace Selector

Google-Style Multi-Account Switcher (sso_accounts)

Click your avatar in the top-right corner to view all signed-in accounts stored in the browser vault, click Add another account to sign into a secondary identity, and switch between accounts with a single click — including automatic JWT expiry validation and token refresh.

Multi-Tenant Workspace Switcher

Developers and consultants often manage Dev, Staging, Production, and multiple client tenants. Use the top-left Tenant Switcher (powered by GET /api/users/tenants and POST /api/tenant-management) to switch workspaces or create a new US/EU tenant in seconds.

4. Self-Service Profile, FIDO2 Passkeys & Active Device Sessions

Navigating to /user-profile empowers every user to manage their own security posture without filing IT tickets:

  • Profile & Avatar Upload: Update personal details (PUT /api/users/self) and upload or crop a profile avatar (POST /api/users/{userId}/avatar).
  • Password Change & MFA Enrollment: Rotate passwords (POST /api/users/self/change-password) and enroll TOTP Authenticator Apps or FIDO2 / WebAuthn Biometric Passkeys (FaceID, TouchID, Windows Hello, YubiKey).
  • Active Device Sessions & Remote Sign-Out: View every active browser/device session with IP address, user-agent, and last-active timestamp (GET /api/users/{userId}/sessions). Users can revoke an unrecognized device immediately (DELETE /api/users/{userId}/sessions/{sessionId}) or click Revoke All Other Sessions (DELETE /api/users/{userId}/sessions/revoke-all).

5. Self-Service GDPR Data Portability & Right to Erasure

When enabled in /settings → Compliance & Privacy, users have built-in regulatory privacy controls on their profile page:

  • Export My Personal Data (GDPR Art. 15 & 20): Calls GET /api/compliance/export-my-data to download a portable JSON package containing their profile attributes, consent history, organization memberships, and login activity.
  • Consent History & Management: View and update privacy policy / terms consent records via GET /api/compliance/consent-status and POST /api/compliance/record-consent.
  • Delete My Account (GDPR Art. 17): Calls DELETE /api/compliance/delete-my-account (after checking tenant ownership via GET /api/users/{userId}/tenant-ownership).

6. Account & Self-Service API Endpoints

Method Endpoint Description
GET https://{your-tenant}.sso.id/api/users/self Returns the authenticated user's profile, roles, MFA status, and preferences.
PUT https://{your-tenant}.sso.id/api/users/self Updates the authenticated user's profile fields (firstName, lastName, phoneNumber).
POST https://{your-tenant}.sso.id/api/users/self/change-password Changes the user's password after verifying currentPassword and tenant password rules.
GET https://{your-tenant}.sso.id/api/users/current/applications Returns all SSO Applications assigned to the current user (directly, via Roles, or via Groups/Orgs).
GET https://{your-tenant}.sso.id/api/users/{userId}/sessions Lists active sessions (DELETE /api/users/{userId}/sessions/{sessionId} revokes one; DELETE .../revoke-all revokes all).
GET https://{your-tenant}.sso.id/api/compliance/export-my-data Downloads GDPR-compliant personal data archive for the logged-in user.
AI Agent Prompt Build a Self-Service User Profile, Active Sessions & App Launcher Page
You are a senior frontend engineer. Build a **Self-Service Account Security & App Launcher Module** connected to **SSO.ID v2** (`https://{your-tenant}.sso.id/api`).

Using the authenticated user's Bearer token (`Authorization: Bearer `), implement:
1. **My Applications Grid**: Fetch `GET https://{your-tenant}.sso.id/api/users/current/applications` and render clickable app launcher cards that redirect to each app's SSO login URL.
2. **Profile & Avatar Editor**: Load `GET /api/users/self`, allow updating profile fields via `PUT /api/users/self`, and upload avatars via `POST /api/users/{userId}/avatar` (`multipart/form-data`).
3. **Active Device Sessions Manager**: Fetch `GET /api/users/{userId}/sessions`, display device/browser/IP/last-active metadata, and provide buttons for single-session revocation (`DELETE /api/users/{userId}/sessions/{sessionId}`) and global sign-out (`DELETE /api/users/{userId}/sessions/revoke-all`).
4. **GDPR Privacy Controls**: Add an "Export My Data (JSON)" button calling `GET /api/compliance/export-my-data` and a "Delete My Account" confirmation modal calling `DELETE /api/compliance/delete-my-account`.