Security Story: Stopping Adversary-in-the-Middle (AiTM) Phishing Cold
How CloudPulse Upgraded from SMS Codes to FIDO2 Passkeys & Multi-Factor Step-Up
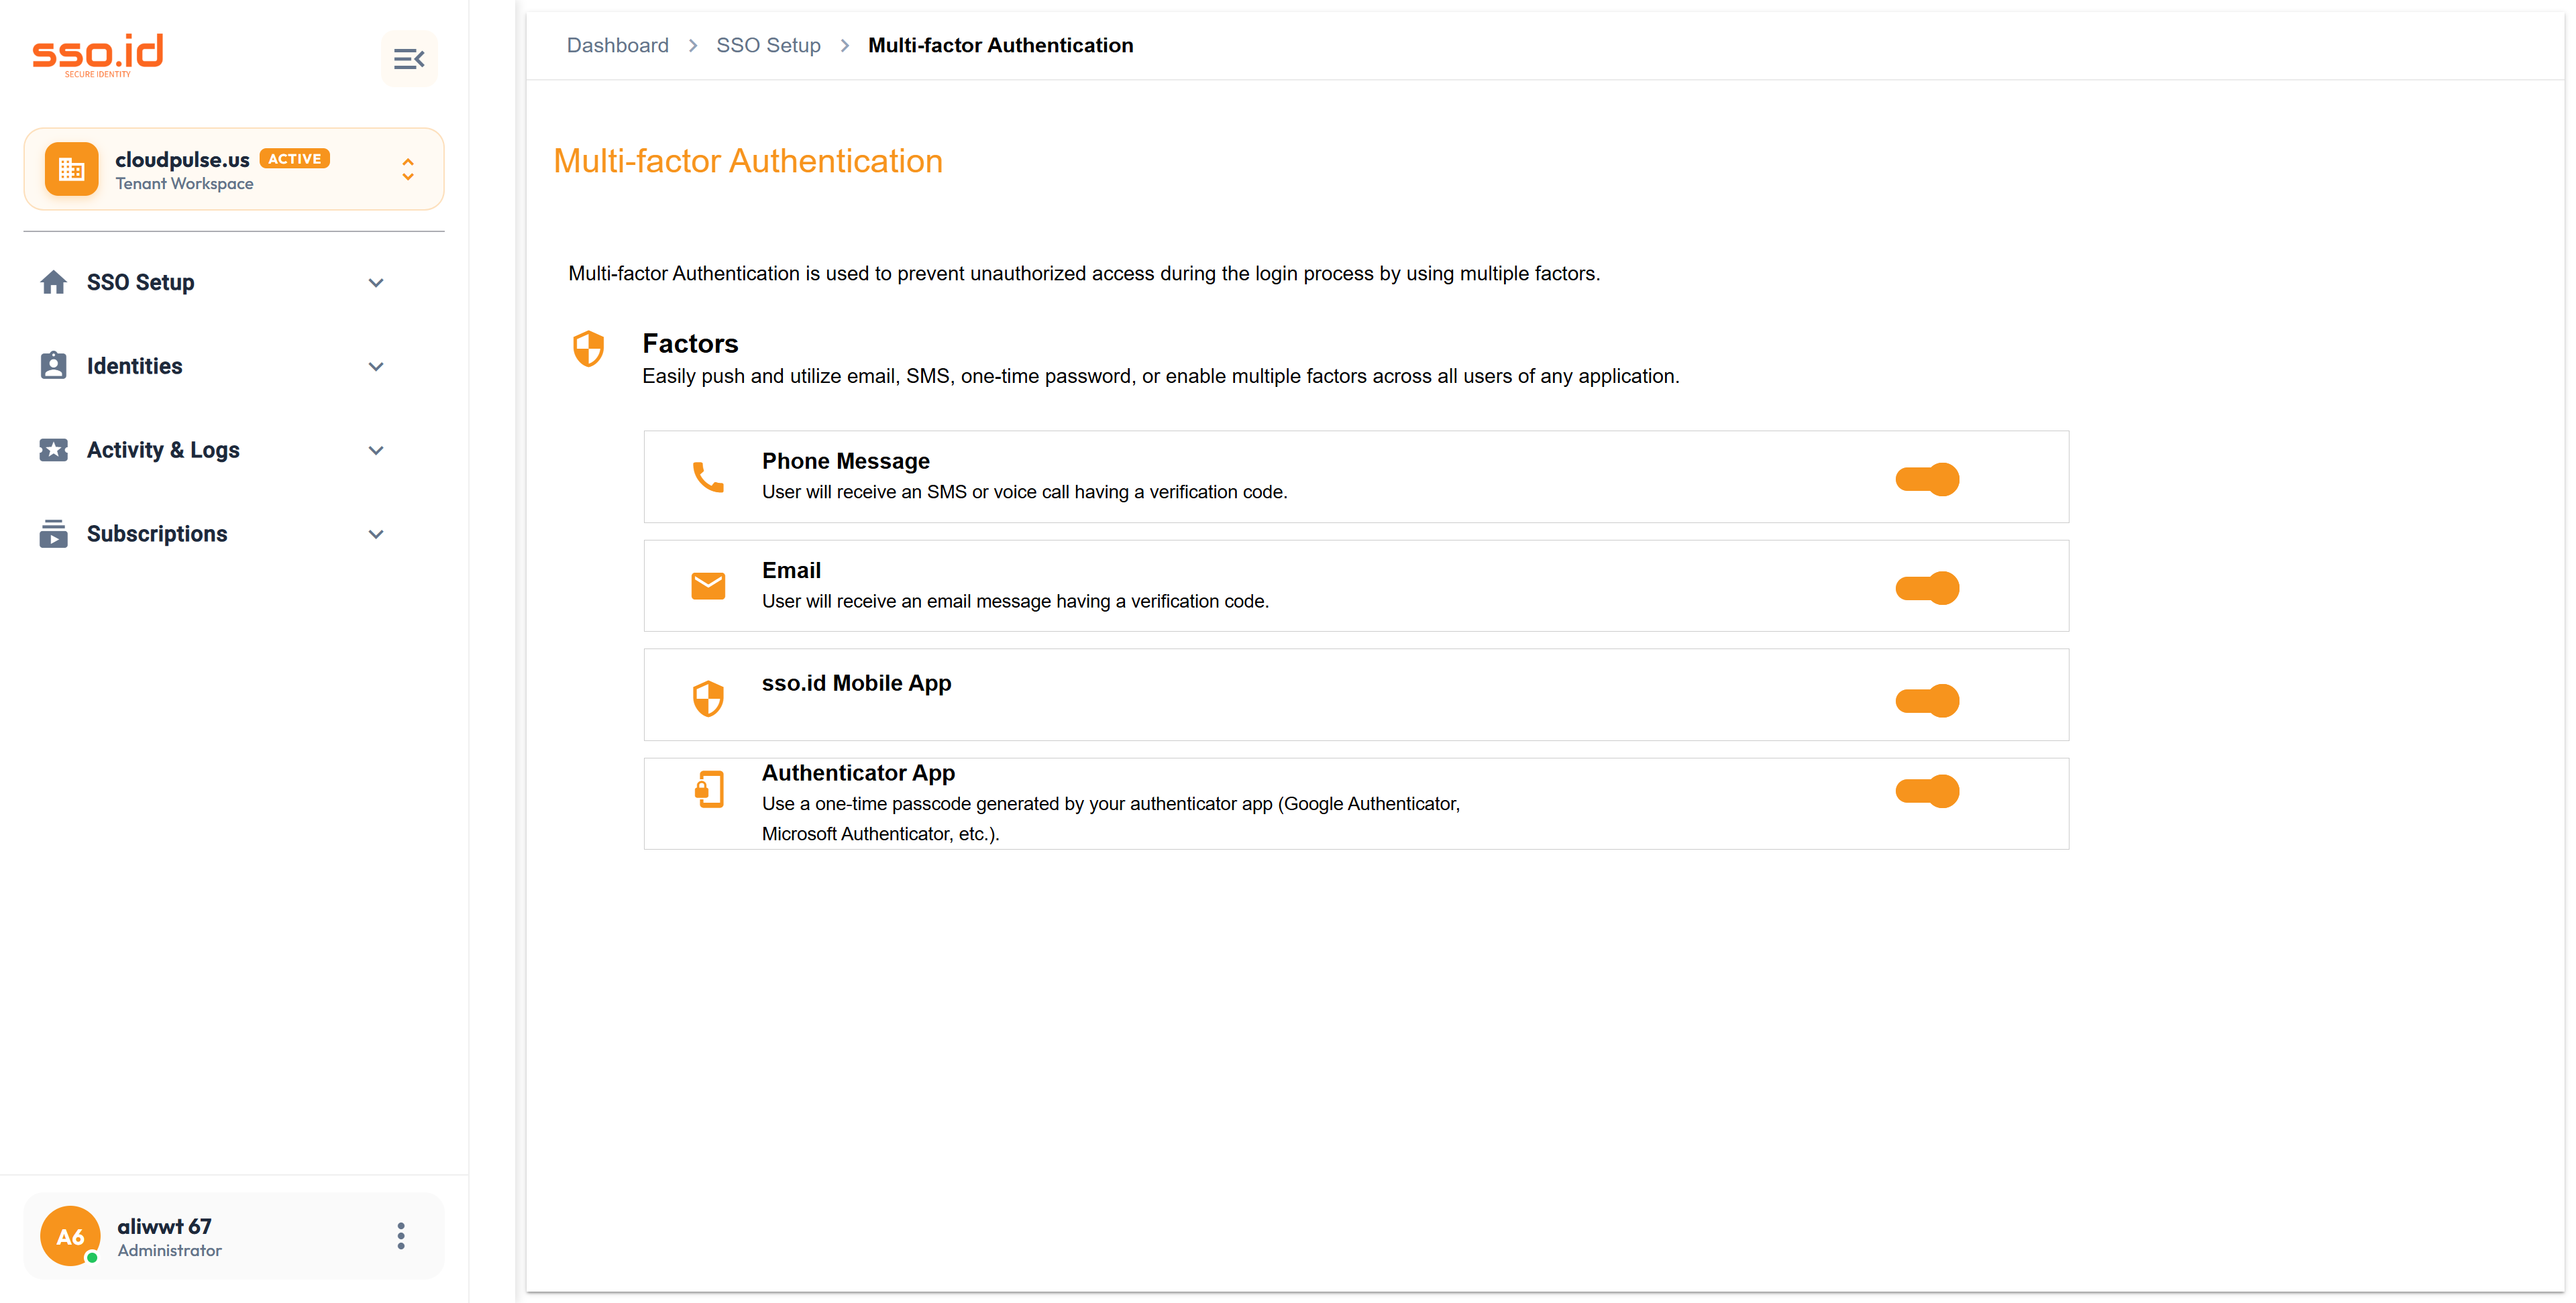
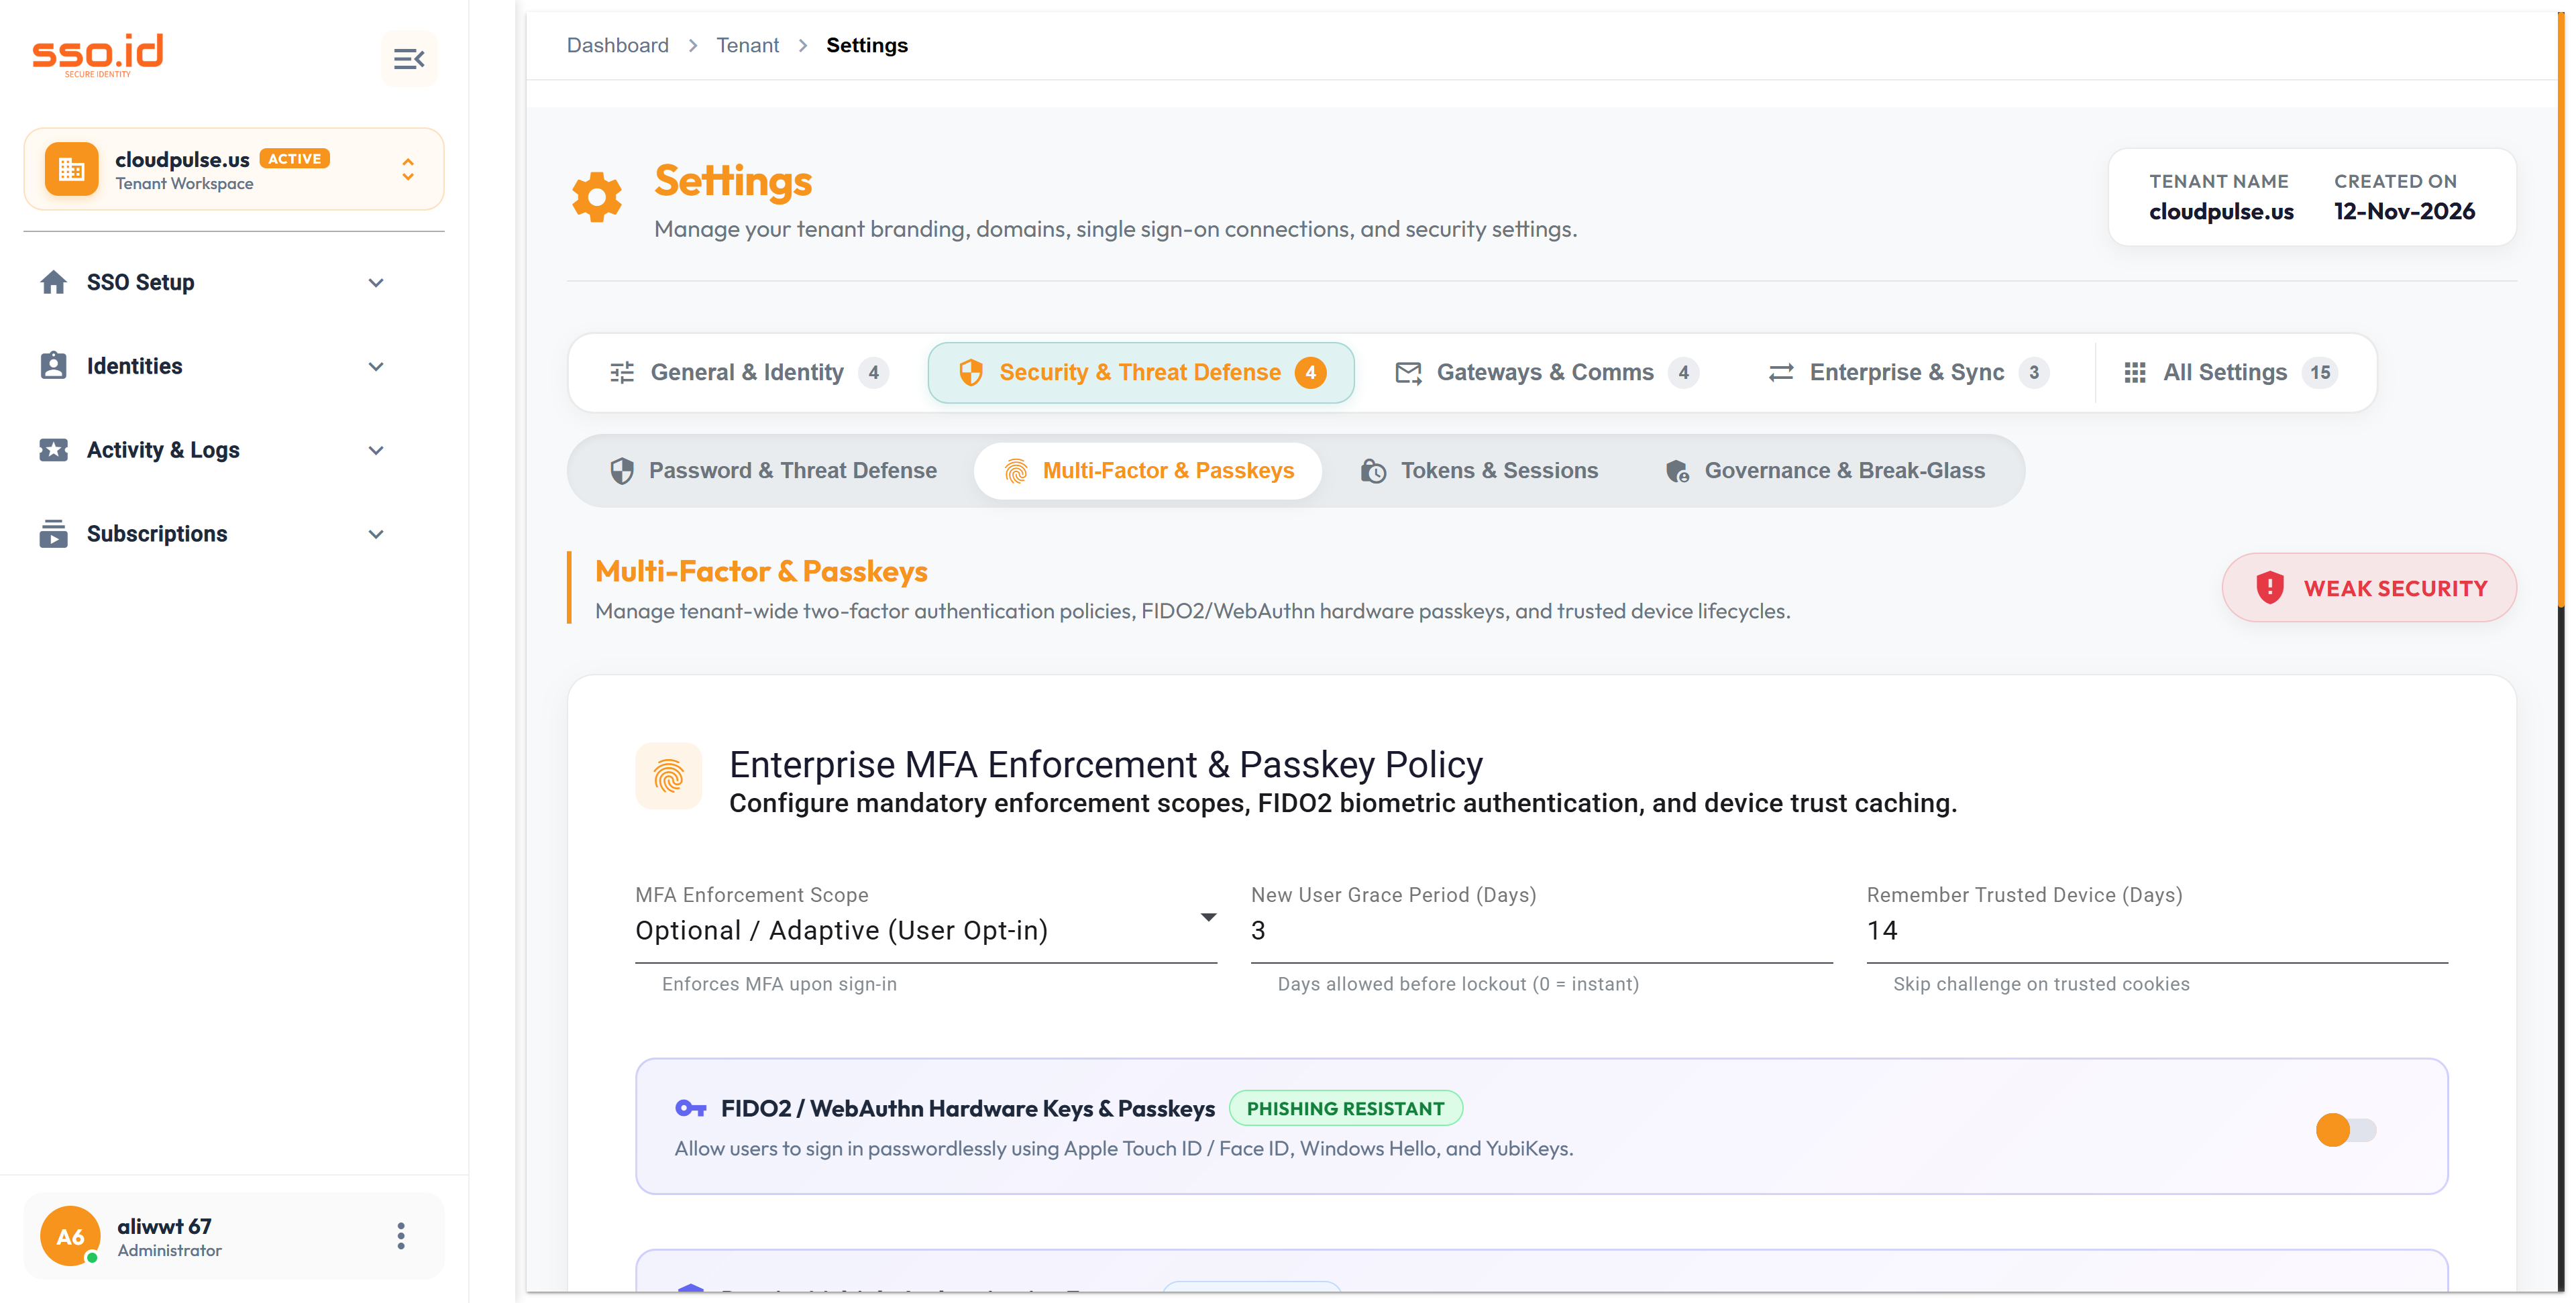
During a red-team penetration test, security researchers attempted a real-time reverse-proxy phishing attack against CloudPulse's administrators. Because CloudPulse had enabled FIDO2 WebAuthn Passkeys (fido2PasskeysEnabled) and Multi-Factor Step-Up (requireMultipleFactors) in /multi-factor and /settings, the browser's hardware enclave cryptographically bound the WebAuthn signature to https://{your-tenant}.sso.id/auth — rendering the phishing proxy 100% useless.